
Commentary | Part II of a series on the MAS Guidelines on AI Risk Management | 7 October 2026 | Luke Soon
Contents
- Introduction
- The Comparative Lens
- Jurisdiction Summaries
- Comparative Table
- The Agent Test
- Points of Convergence
- Points of Divergence
- Implications for Multi-Jurisdictional FIs
- Concluding Observations
I. Introduction
1.1 Part I of this series compared the final MAS Guidelines on Artificial Intelligence Risk Management (AIRG), issued on 7 October 2026, with the November 2025 consultation. Part II places the AIRG alongside the approaches of five other jurisdictions that matter most to financial institutions (FIs) operating in and from Singapore: the European Union, the United Kingdom, the United States, Hong Kong and Australia.
1.2 2026 has been the year in which supervisors moved from principles to expectations. Between April and October, Australia’s prudential regulator wrote to industry on AI, the United States rewrote its model risk guidance, the European Union deferred its high-risk obligations, and Hong Kong announced dedicated guidelines for AI agents. Singapore’s final AIRG completes the set.
1.3 The central finding is that the jurisdictions are converging on what to govern but diverging sharply on how, and most sharply of all on AI agents. Singapore is, as of today, the only one of the six whose financial supervisor has written agent-specific expectations into a single, sector-wide AI risk framework.
1.4 This commentary reflects publicly available material as at 7 October 2026. Several regimes are in motion, and the position may change quickly.
II. The Comparative Lens
2.1 Comparisons of AI regimes often stall on legal form: statute versus guidance. That distinction matters, but it is not what determines the workload inside an FI. This commentary therefore applies six questions to each jurisdiction:
- Instrument. What is the governing text, and is it law, a supervisory statement or a letter?
- Timing. When do expectations bite?
- Scope of AI. Does it reach generative AI and agents, or only conventional models?
- Third-party AI. How does it treat AI procured from, or embedded by, vendors?
- Accountability. Who in the FI is answerable, and to whom?
- Enforceability. Applying the test from Part I: would a supervisor find evidence, or only intentions?
2.2 Particular weight is given to the third question. Agents are where risk is moving fastest, and where the regimes differ most.
III. Jurisdiction Summaries
3.1 Singapore. The AIRG is a single, sector-wide set of supervisory expectations for all FIs, issued on 7 October 2026. Oversight, identification, inventory and materiality apply from 7 October 2027; life cycle controls and capability by 7 October 2028. It covers conventional AI, generative AI and AI agents, including multi-agent systems, and scales expectations by the potential impact of failure. Part I examines it in detail.
3.2 European Union. The AI Act is horizontal legislation, not a financial-sector instrument. Following the Digital Omnibus on AI, which entered into force on 27 July 2026, obligations for stand-alone high-risk systems under Annex III, which include credit scoring, now apply from 2 December 2027 rather than 2 August 2026. High-risk AI embedded in regulated products follows on 2 August 2028. Obligations for general-purpose AI models have applied since August 2025, and the Article 50 transparency obligations were not deferred. The deferral reflects delayed technical standards rather than a softening of intent. The Act regulates by risk tier and role (provider or deployer); it does not contain a dedicated regime for agents.
3.3 United Kingdom. The UK has chosen not to legislate for AI in financial services. The Bank of England and PRA confirmed on 1 April 2026 that they are maintaining a technology-agnostic approach, while keeping further guardrails under review. AI is governed through existing instruments: the PRA’s model risk principles in SS1/23 for banks with internal model approval, the FCA’s Consumer Duty, and the Senior Managers and Certification Regime. AI is a named PRA supervisory priority for 2026, the FCA’s Mills Review is examining AI’s effect on retail markets, and third-party concentration is a stated concern.
3.4 United States. On 17 April 2026, the Federal Reserve, OCC and FDIC replaced SR 11-7 with SR 26-2, revised model risk guidance that is more explicitly risk-based. Its most consequential feature for this comparison is a footnote: generative and agentic AI are described as novel and rapidly evolving, and placed outside the guidance’s scope. Banks are directed to their own risk management practices for those systems, and the agencies have signalled a request for information on AI model risk. Federal guidance is therefore silent on agents for now. Treasury’s financial services AI risk management framework (February 2026) and a Conference of State Bank Supervisors framework (September 2026) partly fill the gap.
3.5 Hong Kong. Hong Kong has no single AI risk framework for FIs. The HKMA has instead led through supervised experimentation, with a GenAI Sandbox whose second cohort covered 27 use cases across 20 banks, extended in March 2026 into a cross-regulator Sandbox++ spanning banking, securities, insurance and MPF. Its supervisory message on accountability is blunt: the HKMA has said it will not accept a machine as an excuse for control failures. The 16 September 2026 Policy Address announced a Commissioner for AI and safety-management guidelines for AI agents, due in 2027, which will apply across sectors.
3.6 Australia. APRA’s letter to industry of 30 April 2026 is its first AI-specific statement of expectations, drawn from a targeted review of large banks, insurers and superannuation trustees. APRA chose not to issue a new standard: existing prudential standards on risk management (CPS 220), operational risk (CPS 230) and information security (CPS 234) already apply to AI. The letter names four weak areas (cyber, governance, supplier risk, and change management and assurance), identifies third-party and supply-chain risk as the widest gap, and observes that identity and access controls have not adapted to non-human actors. It sets no remediation deadline: APRA expects action now and will test it in ordinary supervision.
IV. Comparative Table
4.1 Table 1 applies the six questions in Section II to each jurisdiction.
| Singapore | EU | UK | US | Hong Kong | Australia | |
|---|---|---|---|---|---|---|
| Instrument | AIRG: sector-wide supervisory guidelines | AI Act: horizontal legislation | Existing rules (SS1/23, Consumer Duty, SM&CR) | SR 26-2: interagency model risk guidance | Sandboxes, circulars, reports; no single framework | Letter to industry under CPS 220, 230, 234 |
| Timing | Oct 2027 (governance); Oct 2028 (controls) | Annex III high-risk from Dec 2027 | Ongoing; AI a 2026 supervisory priority | In effect since Apr 2026 | Agent guidelines due 2027 | Immediate; no fixed deadline |
| Generative AI and agents | Named and governed directly | Covered by tier and role; no agent regime | Captured where models fall within existing rules | Expressly out of scope of SR 26-2 | Tested in sandbox; agent guidelines pending | Addressed; non-human identity flagged |
| Third-party AI | FI keeps primary accountability; independent assessment; limit, suspend or replace | Provider and deployer duties allocated by statute | Outsourcing rules; concentration a stated concern | Vendor models within SR 26-2 scope | Existing outsourcing guidance | Supplier risk the widest gap; CPS 230 service provider rules |
| Accountability | Board, senior management, local management for groups | Providers and deployers | Named senior managers under SM&CR | Board and senior management | The machine is not an excuse | Boards and accountable executives |
| Enforceability | High: named owners, evidence trail, phased dates | High: statutory penalties, once in force | Medium: strong for in-scope models and conduct | Mixed: strong for models, absent for agents | Low to medium today; rising | Medium to high: existing standards, active supervision |
V. The Agent Test
5.1 An AI agent is the hardest case for any regime. It acts rather than advises, it calls tools, and its failure mode is not a wrong answer but a wrong sequence of actions. The question for each jurisdiction is simple: if an FI deploys an agent tomorrow, which text tells it what the supervisor expects?
5.2 On that test, the six regimes fall into three groups.
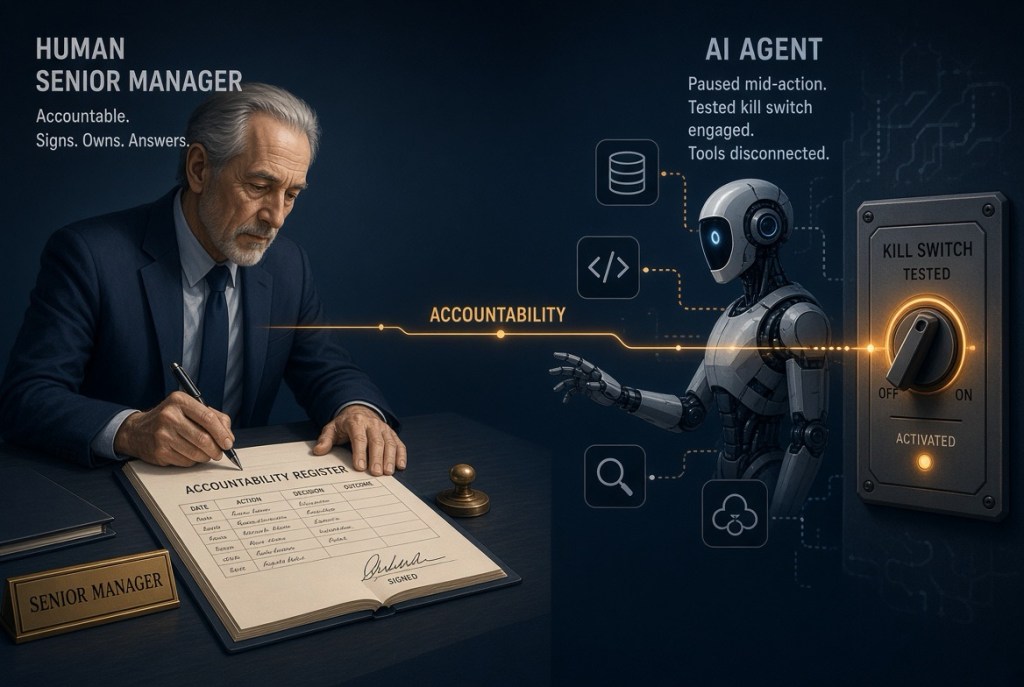
- Named and governed: Singapore. The AIRG names agents and multi-agent systems, and sets agent-specific expectations: inventory of agent identifiers, tool access and guardrails; materiality that scores autonomy; testing of guardrail effectiveness; monitoring of reasoning, actions and tools used; and tested kill switches.
- Acknowledged, not yet specified: Australia and Hong Kong. APRA’s letter recognises that identity and access controls were built for humans, not agents, and expects firms to adapt within existing standards. Hong Kong has run agentic use cases under supervision and has committed to agent guidelines in 2027.
- Covered indirectly or excluded: the EU, UK and US. The EU AI Act governs agents through the risk tier of their use and the role of the firm, not as a category. The UK relies on existing model, conduct and accountability rules. The US has expressly placed agentic AI outside SR 26-2, pending further consultation.
5.3 The US exclusion deserves emphasis. It is a principled choice: the agencies judged the technology too new to prescribe for. But it leaves US banks without federal model risk guidance for the very systems whose risks are rising fastest. Singapore made the opposite choice: write proportionate expectations now, and update them as practice matures (AIRG paragraph 1.12).
5.4 Neither choice is wrong in principle. The practical consequence, however, is that a global FI cannot use its US model risk framework as its agent governance framework. It needs a separate control set for agents, and the AIRG is currently the most complete supervisory statement of what that control set should contain.
VI. Points of Convergence
6.1 Despite different instruments, the regimes agree on more than their legal forms suggest. Four points of convergence stand out.
6.2 Third-party AI is the shared blind spot. Singapore tightened its third-party expectations more than any other area between consultation and final text. APRA found supply-chain risk to be the widest gap in its review. The Bank of England and FCA have both flagged concentration on a small number of AI providers. The EU allocates duties between providers and deployers precisely because so much AI is bought rather than built. Every regime is asking the same question: does the FI understand the AI it did not build?
6.3 You cannot govern what you have not found. Inventories are common ground: the AIRG’s identification and inventory expectations, APRA’s call for an inventory of AI tools and use cases, the model inventories under SS1/23 and SR 26-2, and the EU’s classification of systems by risk tier. Shadow AI and AI embedded in existing platforms are named concerns in both Singapore and Australia.
6.4 Accountability sits with people. No regime accepts that responsibility can be delegated to a system or a vendor. The HKMA’s refusal to accept the machine as an excuse, the UK’s named senior managers, APRA’s accountable executives and the AIRG’s local senior management provisions all express the same principle.
6.5 AI risk is an extension of existing risk. Australia, the UK and the US govern AI largely through existing standards. Singapore’s AIRG says the same in paragraph 1.9, and its drafter makes the point directly. The difference lies in whether the supervisor also writes down what the extension looks like.
VII. Points of Divergence
7.1 The regimes diverge on three matters that will determine how much work an FI must do, and where.
7.2 Legal form. The EU legislates horizontally, with penalties. Singapore and the US issue supervisory guidance. The UK and Australia apply existing rules, clarified by letters and supervisory priorities. Hong Kong leads by experimentation. Legal form shapes the consequence of failure, but it does not reliably predict the depth of expectation: the AIRG, as guidance, is more specific about agents than the AI Act, as law.
7.3 Specificity. Australia and the UK deliberately avoid AI-specific rules; Singapore deliberately writes them. The trade-off is familiar. Technology-agnostic rules age well but leave FIs to infer what good looks like. Specific expectations give clarity today and require updating tomorrow. Singapore has committed to that updating in paragraph 1.12.
7.4 Timing. The effective dates are now staggered across roughly two and a half years:
| Date | Milestone |
|---|---|
| 17 April 2026 | SR 26-2 replaces SR 11-7 in the US |
| 30 April 2026 | APRA letter to industry: expectations apply immediately |
| 2 August 2026 | EU AI Act Article 50 transparency obligations apply |
| 7 October 2027 | AIRG governance and inventory expectations apply |
| 2027 | Hong Kong AI agent guidelines expected |
| 2 December 2027 | EU AI Act Annex III high-risk obligations apply |
| 7 October 2028 | AIRG life cycle controls apply |
7.5 For an FI subject to several regimes, the sequencing matters as much as the content. Australian operations are already being supervised; Singapore governance must be in place by October 2027; EU high-risk credit models follow two months later. A single programme can meet all three only if it is designed against the most demanding requirement in each domain from the outset.
VIII. Implications for Multi-Jurisdictional FIs
8.1 Most FIs headquartered in or operating from Singapore are subject to at least two of these regimes. Running six parallel compliance programmes is neither efficient nor safe: gaps open at the seams. The better design is a single control set, built to the most demanding expectation in each domain and mapped outwards to each regime.
8.2 Table 3 identifies, for each control domain, the regime that currently sets the highest bar.
| Control domain | Highest current bar | Why |
|---|---|---|
| Agent inventory and monitoring | Singapore (AIRG) | Only regime with agent-specific attributes, runtime monitoring and kill switches |
| High-risk use case obligations | EU (AI Act) | Statutory conformity, documentation and human oversight duties for credit scoring and similar uses |
| Model validation for conventional models | US (SR 26-2) and UK (SS1/23) | Mature, detailed validation and model tiering practice |
| Third-party and supply-chain risk | Australia (CPS 230) and Singapore (AIRG) | Binding service provider rules plus explicit AI vendor expectations |
| Individual accountability | UK (SM&CR) | Named, personally accountable senior managers |
| Customer outcomes | UK (Consumer Duty) and Singapore (FEAT) | Outcome-based conduct expectations |
8.3 An FI that meets the AIRG’s agent expectations, the EU’s high-risk duties, US and UK validation standards, Australian supplier rules and UK accountability standards will, in most respects, satisfy all six regimes. This is the design principle behind TrustOS, which maps one layered control architecture to MAS, the EU AI Act, NIST, ISO/IEC 42001 and IMDA’s frameworks among others. The principle matters more than any product: implement once, evidence many times.
8.4 For agents specifically, the practical recommendation is to treat the AIRG as the baseline everywhere. No other regime yet asks for less, and none yet asks for more.
IX. Concluding Observations
9.1 Six regimes, one conclusion: supervisors everywhere now expect FIs to know where their AI is, who owns it, what it depends on, and what happens when it fails. The disagreement is about how much to write down, and when.
9.2 On agents, Singapore has chosen to write it down first. That places Singaporean FIs ahead of the curve and, for a period, on their own. Regulators elsewhere are likely to follow: Hong Kong has committed to agent guidelines, US agencies have promised consultation, and APRA has already identified the gap in identity controls. Firms that build to the AIRG standard now will not need to rebuild when they do.
9.3 Part III of this series will map these regimes in more detail to a single agentic control architecture, layer by layer. Short-term turbulence, for long-term abundance.
References
- Monetary Authority of Singapore, Guidelines on Artificial Intelligence Risk Management, 7 October 2026.
- Gary Ang, Quaintitative, Singapore’s AI Risk Management Guidelines (AIRG) are final, 7 October 2026.
- Orrick, EU AI Act Update: Digital Omnibus Finalizes 8 Compliance Changes, July 2026.
- Gibson Dunn, EU AI Act Omnibus Agreement: Postponed High-Risk Deadlines and Other Key Changes, 2026.
- Global Policy Watch, UK Financial Services Regulators’ Approach to Artificial Intelligence in 2026, April 2026.
- TLT, The Bank of England and PRA set out plans for safe AI innovation, April 2026.
- Meilynx, SR 26-2 and Generative AI: The Carve-Out Explained, 2026.
- RiskTemplate, SR 26-2 Governs Your Models. It Doesn’t Govern Your Generative AI, September 2026.
- King & Wood Mallesons, Gen AI in Financial Services: Latest Regulatory Developments in Hong Kong and Chinese Mainland, 2026.
- The Standard, Banks need take accountability in using AI, says HKMA, January 2026.
- UD, 2026 Policy Address: What It Means for Enterprise AI Strategy, September 2026.
- Clayton Utz, APRA’s AI letter: a shift from framework to targeted expectations, May 2026.
- AegisIQ, APRA’s April 2026 AI Letter, 2026.
The views expressed are the author’s own. This commentary relies on secondary sources for non-Singapore regimes and does not constitute legal or regulatory advice.


Leave a comment